Microsoft Entra Risk Detection Integration Guide🔗
The following instructions are for configuring an integration of Microsoft Entra Risk Detection logs to facilitate ingestion into Secureworks® Taegis™ XDR. For more information, see Entra Identity Protection Risk Detection Overview.
Important
This integration requires a Microsoft Entra premium license.
XDR supports two integration paths for Entra logs:
- (Preferred) Integrate via Azure Event Hubs: This option is preferred due to it providing the fastest and highest throughput of data, however it may incur additional costs to enable.
- Integrate via Microsoft Graph API (REST): This option provides equivalent data to event hubs, but due to the polling nature of a REST-based API in addition to Microsoft rate-limiting, there may be limitations with how quickly data can be collected. See Office 365 and Azure Data Availability for information on our polling practices.
Data Provided from Integration🔗
| Normalized Data | Out-of-the-Box Detections | Vendor-Specific Detections | |
|---|---|---|---|
| MS Azure Active Directory Identity Protection | CloudAudit, Thirdparty |
Note
XDR detectors are not guaranteed to be triggered, even if a data source's logs are normalized to a schema associated with a given detector. However, you can create Custom Detection Rules to generate detections based on normalized data from a data source.
Integrate via Event Hubs🔗
Configure Microsoft Entra Diagnostic Settings🔗
-
Follow the steps in Microsoft's own guide for turning on Entra diagnostic settings: How to stream activity logs to an event hub.
XDR supports normalization of the following Microsoft Entra diagnostic log categories. This includes categories from Microsoft Entra Activity Reports to provide Sophos with contextual information needed for analysis of risk detections:
Note
All other logs will normalize to the
genericschema. A custom parser may be needed to enable normalization of other data sources beyond thegenericschema. It is not recommended to forward metric data to XDR as it will be treated as all other log data and not metrics.
Forward to Event Hub and Enable Integration with XDR🔗
- Once the desired log categories are selected, click Stream to an event hub and enter the desired event hub destination.
- Follow the integration instructions for an event hub to complete the integration with XDR and to begin data ingestion.
Integrate via Microsoft Graph API🔗
Important
Required permissions are documented on the following pages from the Microsoft Graph documentation:
Note
- Azure integrations are supported in US and EU regions, but may not be supported by Microsoft in other regions. Contact Microsoft directly to verify their support of services in other regions.
- The Entra integration via Microsoft Graph API is available for the global Azure cloud. Other national clouds, such as Azure Government, Azure China 21Vianet, and Azure Germany are currently not supported.
Data Availability and Collection Times🔗
Alerts are ingested using the Microsoft REST APIs on a polling basis. For information on data availability, see Office 365 and Azure Data Availability.
Register an Application in Azure🔗
-
Register an application in the Azure portal.
- Name — Any descriptive string
- Supported account types — Accounts in this organizational directory only
Note
Record the following values as they are used to create the integration in XDR:
- Directory (tenant) ID
- Application (client) ID
-
Configure application permissions. The following permission is required:
IdentityRiskEvent.Read.All(application permission)
-
Click Grant admin consent for <Azure tenant name>.
-
Provide credentials for the application by uploading a certificate.
Important
Certificates will expire and need to be renewed both with Microsoft Entra ID and with XDR to allow for continued functionality before their expiration date.
Important
XDR supports ONLY the Privacy-Enhanced Mail (PEM) format. More information on the PEM format can be found in RFC 7468.
Encrypted keys and client secrets are NOT supported.
Note
Self-signed certificates are supported.
Use one of the following commands to generate a self-signed PEM (.pem extension) certificate using PowerShell or OpenSSL:
# Prompt user for input

$certname = Read-Host -Prompt "Enter certificate name"
$keyname = Read-Host -Prompt "Enter key name"
$mypwd = Read-Host -Prompt "Enter password" -AsSecureString
$location = Read-Host -Prompt "Enter location"
$cert = New-SelfSignedCertificate -Subject "CN=$certname" -CertStoreLocation "Cert:\CurrentUser\My" -KeyExportPolicy Exportable -KeySpec Signature -KeyLength 2048 -KeyAlgorithm RSA -HashAlgorithm SHA256
Export-PfxCertificate -Cert $cert -FilePath "$location\$certname.pfx" -Password $mypwd
Install-Module -Name PSPKI -Scope CurrentUser
Import-Module -Name PSPKI
Convert-PfxToPem -InputFile "$location\$certname.pfx" -Outputfile "$location\$certname.pem"
# Read the PEM file content

$pemContent = Get-Content "$location\$certname.pem" -Raw
# Extract private key and certificate

$privateKey = $pemContent -replace "(?ms).*?(-----BEGIN PRIVATE KEY-----.+?-----END PRIVATE KEY-----).*", '$1'
$certificate = $pemContent -replace "(?ms).*?(-----BEGIN CERTIFICATE-----.+?-----END CERTIFICATE-----).*", '$1'
# Save private key and certificate to separate files

$privateKey | Set-Content "$location\$keyname.pem"
$certificate | Set-Content "$location\$certname.pem"
Write-Host "Files located at: $location"
pause
Note
Copy and paste the preceding code into a text file, save the file with a .ps1 extension (e.g., CertGen.ps1), and run the script using PowerShell.
Note
Depending on the PowerShell version being used, you may need to replace -Subject with -SubjectName if there are any errors with -Subject.
Add Integration in XDR🔗
- From the Taegis Menu, go to Integrations > Cloud APIs.
-
Click Add an Integration from the top of the page.

Add an Integration -
From the Optimized tab, click Office 365/Azure.
-
Choose Set Up under Microsoft Entra Risk Detection.
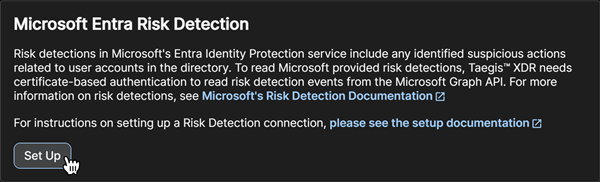
Create the Integration -
Enter a name for the integration. This can be any string.
- Enter the Tenant ID and the Application Client ID from Step 1 in the Register an Application in Azure section.
-
Upload the certificate and its associated private key.
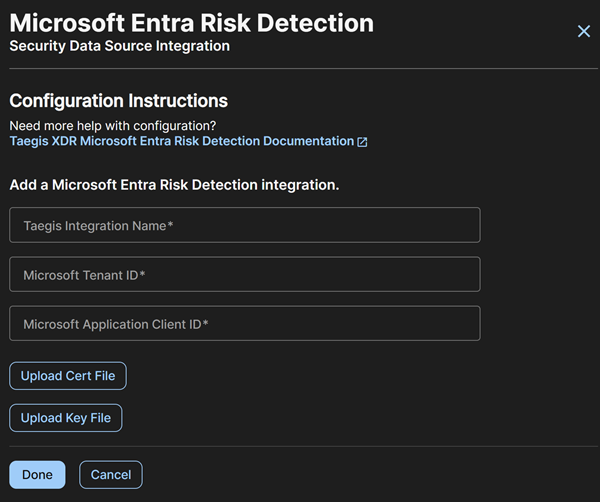
Complete the Integration -
Select Done to complete the integration with XDR.